Форум
[РЕШЕНО] Как FreeRDP подключить через VPN ?
всем доброго!
подскажите пожалуйста как выкрутиться из ситуёвины.
подключаюсь к компу в московском офисе из офиса саратовского через фриРДП:
xfreerdp /u:ЛОГИН /p:ПАРОЛЬ /v:ts.РАБОТА.ruмежду офисами прокинуто VPN и всё отлично подключается
чтобы подключиться из дома, нужно сначала законектится к vpn.РАБОТА.ru, а потом через него прокинуть рдп-шку на ts.РАБОТА.ru
подскажите пожалуйста как быть.
vpn.РАБОТА.ru, после логина долго пытается определить ОС и предлагает установить "AnyConnect Secure Mobility Client"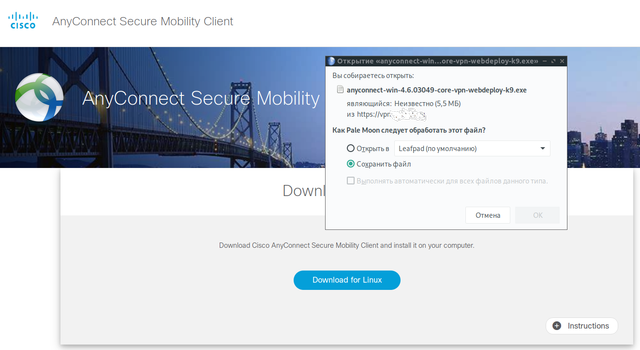
:lol: для винды
никогда не имел дела с подобными вещами, в репах вижу полно всяких vpn-* плагинов, клиентов и прочего...
как тут быть-то подскажите пожалуйста.
таки ой! запалился ))
век живи, век учись..
оказывается для циски нужен свой клиент, тот самый, что предлагают скачать.
в репах что-то есть:
extra/openconnect 1:8.03-1
    Open client for Cisco AnyConnect VPN
aur/anyconnect-client 4.5.04029-3 (2) (0,22)
    Cisco AnyConnect Secure Mobility Client
aur/cisco-anyconnect 4.7.00136-1 (0) (0,00)
    Cisco AnyConnect Secure Mobility Client
aur/openconnect-git 7.08.r127.g8977877-1 [installed: 8.03.r37.g49fbe6f1-1] (9) (0,03)
    Open client for Cisco AnyConnect VPN
и оно вроде как работает: спрашивает группу, логин, пароль и создаёт новый интерфейс каждый раз с разным IP:
tun0: flags=4305<UP,POINTOPOINT,RUNNING,NOARP,MULTICAST>  mtu 1200
        inet 192.168.202.110  netmask 255.255.255.255  destination 192.168.202.110
        unspec 00-00-00-00-00-00-00-00-00-00-00-00-00-00-00-00  txqueuelen 500  (UNSPEC)
        RX packets 0  bytes 0 (0.0 B)
        RX errors 0  dropped 0  overruns 0  frame 0
        TX packets 0  bytes 0 (0.0 B)
        TX errors 0  dropped 0 overruns 0  carrier 0  collisions 0
вот как теперь freerdp2 через него прокинуть, - загадка
Добавлено позже:
man у него кривой, но есть хелпСпойлер
FreeRDP - A Free Remote Desktop Protocol Implementation
See www.freerdp.com for more information
Usage: xfreerdp [file] [options] [/v:<server>[:port]]
Syntax:
/flag (enables flag)
/option:<value> (specifies option with value)
+toggle -toggle (enables or disables toggle, where '/' is a synonym of '+')
/a:<addin>[,<options>] Addin
/action-script:<file-name> Action script
/admin Admin (or console) session
+aero Enable desktop composition
/app:<path> or ||<alias> Remote application program
/app-cmd:<parameters> Remote application command-line parameters
/app-file:<file-name> File to open with remote application
/app-guid:<app-guid> Remote application GUID
/app-icon:<icon-path> Remote application icon for user interface
/app-name:<app-name> Remote application name for user interface
/assistance:<password> Remote assistance password
+async-channels Enable Asynchronous channels (experimental)
+async-input Enable Asynchronous input
+async-update Enable Asynchronous update
/audio-mode:<mode> Audio output mode
+auth-only Enable Authenticate only
-authentication Disable Authentication (expermiental)
+auto-reconnect Enable Automatic reconnection
/auto-reconnect-max-retries:... Automatic reconnection maximum retries, 0 for unlimited [0,1000]
-bitmap-cache Disable bitmap cache
/bpp:<depth> Session bpp (color depth)
/buildconfig Print the build configuration
/cert-ignore Ignore certificate
/cert-name:<name> Certificate name
/cert-tofu Automatically accept certificate on first connect
/client-hostname:<name> Client Hostname to send to server
-clipboard Disable Redirect clipboard
/codec-cache:rfx|nsc|jpeg Bitmap codec cache
-compression Disable compression
/compression-level:<level> Compression level (0,1,2)
+credentials-delegation Enable credentials delegation
/d:<domain> Domain
-decorations Disable Window decorations
/disp Display control
/drive:<name>,<path> Redirect directory <path> as named share <name>
+drives Enable Redirect all mount points as shares
/dvc:<channel>[,<options>] Dynamic virtual channel
/dynamic-resolution Send resolution updates when the window is resized
/echo Echo channel
-encryption Disable Encryption (experimental)
/encryption-methods:... RDP standard security encryption methods
/f Fullscreen mode (<Ctrl>+<Alt>+<Enter> toggles fullscreen)
-fast-path Disable fast-path input/output
+fipsmode Enable FIPS mode
-floatbar Disable floatbar in fullscreen mode
+fonts Enable smooth fonts (ClearType)
/frame-ack:<number> Number of frame acknowledgement
/from-stdin[:force] Read credentials from stdin. With <force> the prompt is done before connection, otherwise on server request.
/g:<gateway>[:<port>] Gateway Hostname
/gateway-usage-method:direct|detect Gateway usage method
/gd:<domain> Gateway domain
/gdi:sw|hw GDI rendering
/geometry Geometry tracking channel
+gestures Enable Consume multitouch input locally
/gfx[:RFX|AVC420|AVC444] RDP8 graphics pipeline (experimental)
/gfx-h264[:AVC420|AVC444] RDP8.1 graphics pipeline using H264 codec
+gfx-progressive Enable RDP8 graphics pipeline using progressive codec
+gfx-small-cache Enable RDP8 graphics pipeline using small cache mode
+gfx-thin-client Enable RDP8 graphics pipeline using thin client mode
+glyph-cache Enable Glyph cache (experimental)
/gp:<password> Gateway password
-grab-keyboard Disable Grab keyboard
/gt:rpc|http|auto Gateway transport type
/gu:... Gateway username
/gat:<access token> Gateway Access Token
/h:<height> Height
+heartbeat Enable Support heartbeat PDUs
/help Print help
+home-drive Enable Redirect user home as share
/ipv6 Prefer IPv6 AAA record over IPv4 A record
/kbd:0x<id> or <name> Keyboard layout
/kbd-fn-key:<value> Function key value
/kbd-list List keyboard layouts
/kbd-subtype:<id> Keyboard subtype
/kbd-type:<id> Keyboard type
/load-balance-info:<info-string> Load balance info
/log-filters:... Set logger filters, see wLog(7) for details
/log-level:... Set the default log level, see wLog(7) for details
/max-fast-path-size:<size> Specify maximum fast-path update size
/max-loop-time:<time> Specify maximum time in milliseconds spend treating packets
+menu-anims Enable menu animations
/microphone[:...] Audio input (microphone)
/monitor-list List detected monitors
/monitors:<id>[,<id>[,...]] Select monitors to use
-mouse-motion Disable Send mouse motion
/multimedia[:...] Redirect multimedia (video)
/multimon[:force] Use multiple monitors
+multitouch Enable Redirect multitouch input
+multitransport Enable Support multitransport protocol
-nego Disable protocol security negotiation
/network:... Network connection type
/nsc NSCodec support
-offscreen-cache Disable offscreen bitmap cache
/orientation:0|90|180|270 Orientation of display in degrees
+old-license Enable Use the old license workflow (no CAL and hwId set to 0)
/p:<password> Password
/parallel[:<name>[,<path>]] Redirect parallel device
/parent-window:<window-id> Parent window id
+password-is-pin Enable Use smart card authentication with password as smart card PIN
/pcb:<blob> Preconnection Blob
/pcid:<id> Preconnection Id
/pheight:<height> Physical height of display (in millimeters)
/play-rfx:<pcap-file> Replay rfx pcap file
/port:<number> Server port
+print-reconnect-cookie Enable Print base64 reconnect cookie after connecting
/printer[:<name>[,<driver>]] Redirect printer device
/proxy:... Proxy settings: override env.var (see also environment variable below).
Protocol "socks5" should be given explicitly where "http" is default.
Note: socks proxy is not supported by env. variable
/pth:<password-hash> Pass the hash (restricted admin mode)
/pwidth:<width> Physical width of display (in millimeters)
/reconnect-cookie:<base64-cookie> Pass base64 reconnect cookie to the connection
/redirect-prefer:... Override the preferred redirection order
/relax-order-checks Do not check if a RDP order was announced during capability exchange, only use when connecting to a buggy server
/restricted-admin Restricted admin mode
/rfx RemoteFX
/rfx-mode:image|video RemoteFX mode
/scale:100|140|180 Scaling factor of the display
/scale-desktop:<percentage> Scaling factor for desktop applications (value between 100 and 500)
/scale-device:100|140|180 Scaling factor for app store applications
/sec:rdp|tls|nla|ext Force specific protocol security
+sec-ext Enable NLA extended protocol security
-sec-nla Disable NLA protocol security
-sec-rdp Disable RDP protocol security
-sec-tls Disable TLS protocol security
/serial[:...] Redirect serial device
/shell:<shell> Alternate shell
/shell-dir:<dir> Shell working directory
/size:... Screen size
/smart-sizing[:<width>x<height>] Scale remote desktop to window size
/smartcard[:<str>[,<str>…]] Redirect the smartcard devices containing any of the <str> in their names.
/smartcard-logon Activates Smartcard Logon authentication. (EXPERIMENTAL: NLA not supported)
/sound[:...] Audio output (sound)
/span Span screen over multiple monitors
/spn-class:<service-class> SPN authentication service class
/ssh-agent SSH Agent forwarding channel
/t:<title> Window title
-themes Disable themes
/tls-ciphers:netmon|ma|ciphers Allowed TLS ciphers
/tls-seclevel:<level> TLS security level - defaults to 1
-toggle-fullscreen Disable Alt+Ctrl+Enter toggles fullscreen
/u:... Username
+unmap-buttons Enable Let server see real physical pointer button
/usb:... Redirect USB device
/v:<server>[:port] Server hostname
/vc:<channel>[,<options>] Static virtual channel
/version Print version
/video Video optimized remoting channel
/vmconnect[:<vmid>] Hyper-V console (use port 2179, disable negotiation)
/w:<width> Width
-wallpaper Disable wallpaper
+window-drag Enable full window drag
/window-position:<xpos>x<ypos> window position
/wm-class:<class-name> Set the WM_CLASS hint for the window instance
/workarea Use available work area
Examples:
xfreerdp connection.rdp /p:Pwd123! /f
xfreerdp /u:CONTOSO\JohnDoe /p:Pwd123! /v:rdp.contoso.com
xfreerdp /u:JohnDoe /p:Pwd123! /w:1366 /h:768 /v:192.168.1.100:4489
xfreerdp /u:JohnDoe /p:Pwd123! /vmconnect:C824F53E-95D2-46C6-9A18-23A5BB403532 /v:192.168.1.100
Clipboard Redirection: +clipboard
Drive Redirection: /drive:home,/home/user
Smartcard Redirection: /smartcard:<device>
Serial Port Redirection: /serial:<name>,<device>,[SerCx2|SerCx|Serial],[permissive]
Serial Port Redirection: /serial:COM1,/dev/ttyS0
Parallel Port Redirection: /parallel:<name>,<device>
Printer Redirection: /printer:<device>,<driver>
Audio Output Redirection: /sound:sys:oss,dev:1,format:1
Audio Output Redirection: /sound:sys:alsa
Audio Input Redirection: /microphone:sys:oss,dev:1,format:1
Audio Input Redirection: /microphone:sys:alsa
Multimedia Redirection: /multimedia:sys:oss,dev:/dev/dsp1,decoder:ffmpeg
Multimedia Redirection: /multimedia:sys:alsa
USB Device Redirection: /usb:id,dev:054c:0268
For Gateways, the https_proxy environment variable is respected:
export https_proxy=http://proxy.contoso.com:3128/
xfreerdp /g:rdp.contoso.com ...
More documentation is coming, in the meantime consult source files
вот интересно, это имеет онтношение к моему затыку или нет?
"""
For Gateways, the https_proxy environment variable is respected:
    export https_proxy=http://proxy.contoso.com:3128/
    xfreerdp /g:rdp.contoso.com ...
"""
Добавлено позже:
что-то начало получаться, но.... фэйл
~$ xfreerdp /g:ИП:443 /u:ЛОГИН /p:ПАРОЛЬ /v:ts.РАБОТА.ru
[10:23:38:317] [9828:9829] [INFO][com.freerdp.client.common.cmdline] - loading channelEx cliprdr
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - @@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - @           WARNING: CERTIFICATE NAME MISMATCH!           @
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - @@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@@
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - The hostname used for this connection (ИП:443)
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - does not match any of the names given in the certificate:
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - Common Name (CN):
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - 	vpn.РАБОТА.ru
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - Alternative names:
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - 	 vpn.РАБОТА.ru
[10:23:38:469] [9828:9829] [ERROR][com.freerdp.crypto] - A valid certificate for the wrong name should NOT be trusted!
Certificate details:
	Subject: C = RU, L = Moscow, O = JSC R-РАБОТА, OU = IT Department, CN = vpn.РАБОТА.ru
	Issuer: C = US, O = DigiCert Inc, OU = www.digicert.com, CN = GeoTrust RSA CA 2018
	Thumbprint: xx:xx:xx:xx:СЕРТИФИКАТ:xx:xx:xx:xx:*
The above X.509 certificate could not be verified, possibly because you do not have
the CA certificate in your certificate store, or the certificate has expired.
Please look at the OpenSSL documentation on how to add a private CA to the store.
Do you trust the above certificate? (Y/T/N) Y
[10:23:42:745] [9828:9829] [ERROR][com.freerdp.core.nego] - Protocol Security Negotiation Failure
[10:23:42:745] [9828:9829] [ERROR][com.freerdp.core] - freerdp_set_last_error ERRCONNECT_SECURITY_NEGO_CONNECT_FAILED [0x0002000C]
[10:23:42:745] [9828:9829] [ERROR][com.freerdp.core.connection] - Error: protocol security negotiation or connection failureПроблема оказалась очень легко решаемой, правда пришлось поставить НетворкМанагер, чего я очень долго не хотел по религиозным соображениям))
Но, работодатель перевёл нас на хоум-офис.
Припёрло.
sudo pacman -S networkmanager nm-connection-editor network-manager-applet networkmanager-openconnectОстанавливаем прежнего юнита, ибо будут конфликты
sudo systemctl disable dhcpcd.serviceЗапускаем юнита нового
sudo systemctl enable NetworkManager.serviceДалее настройка
ЛКМ на значке НМ в трее -> Соединения VPN -> Настроить VPN... -> Создаём новое соединение:
пишем Имя соединения: Работа
выбираем VPN Protocol : "Циско ЭниКоннект..."
пишем Шлюз: vpn.работа.ру
больше заполнять в моей ничего не потребовалось.
Сохраняем, закрываем.
ЛКМ на значке НМ в трее -> Соединения VPN -> ставим галочку напротив соединения "Работа"
Проходим авторизацию в появившемся диалоговом окне, на значке в трее появился маленький "замочек".
Готово.
Подключаемся предпочитаемым образом, например: xfreerdp /u:ЛОГИН /p:ПАРОЛЬ /v:ts.РАБОТА.ru /прочие опции
только бы не поломали
https://www.opennet.ru/opennews/art.shtml?num=52712
изменился синтаксис парама для сертификатов
/cert:[deny,ignore,name:name,tofu,fingerprint:hash:hash as
       hex[,fingerprint:hash:another hash]]
           Certificate accept options. Use with care! * deny ... Automatically
           abort connection if the certificate does not match, no user
           interaction. * ignore ... Ignore the certificate checks altogether
           (overrules all other options) * name ... Use the alternate <name<
           instead of the certificate subject to match locally stored
           certificates * tofu ... Accept certificate unconditionally on first
           connect and deny on subsequent connections if the certificate does
           not match * fingerprints ... A list of certificate hashes that are
           accepted unconditionally for a connection

       /cert-deny
           [deprecated, use /cert:deny] Automatically abort connection for any
           certificate that can not be validated.

       /cert-ignore
           [deprecated, use /cert:ignore] Ignore certificate

       /cert-name:name
           [deprecated, use /cert:name:<name<] Certificate name

       /cert-tofu
           [deprecated, use /cert:tofu] Automatically accept certificate on
           first connect
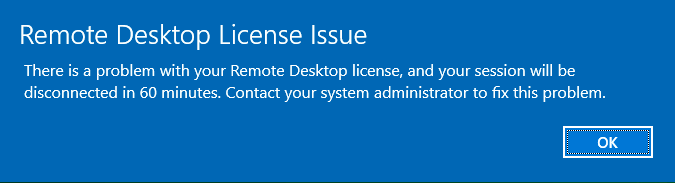
и странность на удалённой винде (возможно совпадение), но на старую версию не буду откатываться пока, возможно действительно админы что-то админят.
Добавлено позже:
откатил на старую версию freerdp-1:2.0.0_rc4-8-x86_64.pkg.tar.zst
синяя табличка не выскакивает.